
There's a new bug reported in the way Firefox handles writes to the
'location.hostname' DOM property. The vulnerability could
potentially allow a malicious website to manipulate the
authentication cookies for a third-party site.
The bug could allow for the browser to appear as if were connecting
to a bank, when in fact it would instead be receiving data from a
bad guy.
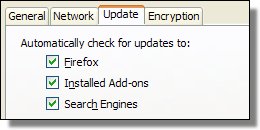
Firefox is often patched quickly, so take note, it's an excellent
idea to enable Firefox's automatic updates option if you haven't
already.
A demo of the vulnerability and a suggested work-around can be
found here