New variants of Storm Worm have started to use kernel-mode
rootkit techniques to hide their files, registry keys and active
network connections. F-Secure BlackLight is able to detect the
hidden files.
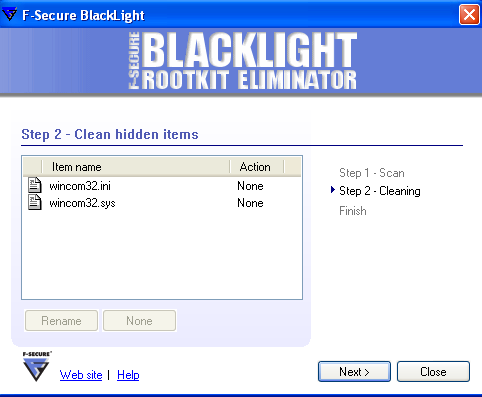
These variants are now detected
as W32/Stormy.AB and
Trojan-Downloader.Win32.Agent.bet.